Third-party due diligence in 2026: do you really know who owns your vendor?
·17 min de lecture
Marc Seitz
Third party due diligence is the risk-based screening of the vendors, suppliers, agents, distributors and joint-venture partners a company works with, run before a contract is signed and repeated for as long as the relationship lasts. It answers one thing: does this counterparty create exposure the company would be held responsible for?
Quick recap
Third party due diligence screens vendors, agents and partners continuously, unlike M&A due diligence, which reviews one target once before a transaction closes.
It also collides with sell-side vendor due diligence, the report a seller commissions on its own business for bidders, which is a different workstream entirely.
Risk tiering comes first: jurisdiction, sector, spend, public-official contact and data access decide whether a counterparty gets screening only, a standard review, or enhanced diligence.
A programme covers 9 domains: sanctions screening, beneficial ownership, adverse media, bribery and corruption, financial health, information security, data protection, modern slavery, and continuity and insurance.
Under the OFAC 50 percent rule, an entity owned 50 percent or more in aggregate by blocked persons is itself blocked, even when its own name is on no list.
EU anti-money-laundering rules use a 25 percent shareholding to identify an ultimate beneficial owner, and the German Supply Chain Due Diligence Act has covered companies with 1,000 or more employees in Germany since 1 January 2024.
Automated screening costs roughly $200 to $500 per counterparty, manual review of the evidence around $1,000, and enhanced diligence several thousand.
A data room for third party due diligence is the evidence repository, not the questionnaire tool: it holds the certificates and ownership charts a questionnaire only claims exist.
Papermark runs a data room for third party due diligence with granular permissions, dynamic watermarking, per-visitor analytics and file requests from counterparties, from €99/month.
Most companies find the weak point the same way. An internal audit asks for the evidence behind a supplier approval from two years ago and nobody can produce it: the questionnaire sits in a workflow tool, the certificates are in three inboxes, and the approver has left. The screening happened; the record did not survive.
That is a document problem before it is a compliance problem. A data room for third party due diligence keeps the evidence in one place, with a link for each internal reviewer and an upload folder for each counterparty. Section 10 covers the setup.
1. What is third party due diligence?
Third party due diligence is the process of investigating an external counterparty before you engage them commercially and re-checking them for as long as the relationship continues. In scope are the counterparties who act for you or touch your operations: suppliers, subcontractors, resellers, distributors, sales agents, customs brokers, consultants and joint-venture partners. The output is a decision to approve, approve with conditions, or decline, backed by a file of evidence explaining why.
The workstream exists because liability travels. Under most anti-bribery regimes a company can be prosecuted for a payment made by an agent it never instructed, and under sanctions rules a payment routed to a company owned by a blocked person is a violation regardless of intent. Data protection law makes a controller answerable for its processors, and supply chain legislation makes a manufacturer answerable for labour conditions at a supplier it has never seen.
Three things get confused in search results. M&A due diligence is a transaction review: an acquirer investigates one target, once, to price a deal. Vendor due diligence in the sell-side sense is the report a seller commissions on its own business so bidders read a prepared analysis. Third party due diligence is neither. It is a continuous programme across hundreds or thousands of counterparties, owned by compliance and procurement rather than a deal team, with no closing date. Our vendor due diligence checklist covers the buy-side version in more detail.
2. Risk tiering: the step that decides how much diligence a counterparty gets
No programme reviews every counterparty to the same depth, and any that claims to is wasting money. A company with 600 active suppliers cannot run enhanced diligence on all of them. The stationery supplier and the customs agent who deals daily with port officials in a high-corruption jurisdiction present entirely different risk.
Tiering is where that judgement gets written down. The inputs are consistent across most programmes: the countries the counterparty operates from, the sector, annual spend, whether it interacts with public officials on your behalf, whether it processes personal data or connects to your systems, and whether it is a single source for something you cannot run without.
Tiering deserves its own documented step because regulators ask about the method rather than the result. Anti-bribery guidance consistently expects a documented, risk-based approach. A programme that can show why a counterparty landed in the low tier is defensible; one that screened everything at the same shallow depth is not, even if it caught nothing.
Tier
What puts a counterparty here
Depth of review
Refresh cadence
Tier 1, high
Public-official contact, high-corruption jurisdiction, or critical system access
Enhanced: verified ownership, adverse media, interview or site visit
Annual, with continuous screening
Tier 2, medium
Material spend, regulated service, personal data processing, no official contact
Standard: questionnaire plus evidence review and financial check
Every 2 years, with continuous screening
Tier 3, low
Low spend, commodity goods, no data access, low-risk jurisdiction
Single-source supplier for a process the business cannot run without
Adds continuity, insurance and financial health review
Annual regardless of risk tier
Cadence matters more than initial depth: a Tier 1 counterparty reviewed in 2024 and never revisited is, by 2026, unreviewed.
3. The 9 domains of a third party due diligence review
The nine domains below cover what a mature programme checks. Not every domain applies to every counterparty, which is the point of tiering, but the list is the menu each tier draws from. Compliance owns the first four, security and privacy the next two, finance and operations the last three, which already tells you the evidence has more than one internal audience.
The integrity checks come first. Sanctions and watchlist screening asks whether the entity, its owners or its officers appear on a restricted list. Beneficial ownership asks who ultimately controls the counterparty, and it gets section 4 to itself because it is where programmes most often fail. Anti-bribery and corruption checks for a policy, training records and a gifts register, and asks whether the commercial model creates temptation.
The technical checks apply whenever a counterparty touches data or systems. Information security asks for a current SOC 2 Type II report or ISO 27001 certificate with a scope statement you have actually read. Data protection asks for a processing agreement, a sub-processor list, a transfer mechanism for data leaving the EU, and breach history, because GDPR gives a controller 72 hours to notify a supervisory authority and that clock starts when the processor tells you. The overlap with IT due diligence is real, though this version repeats far more often. The last three domains are commercial: solvency, labour and sub-tier sourcing, and whether continuity plans and insurance match the contract.
Ownership chart, registry extracts, signed UBO declaration
Compliance
3
Adverse media
Litigation history, regulator correspondence, self-disclosure form
Compliance and legal
4
Bribery and corruption
ABAC policy, code of conduct, training records, gifts register
Legal
5
Information security
SOC 2 Type II report, ISO 27001 certificate, penetration test summary
Security
6
Data protection
DPA, sub-processor list, transfer mechanism, breach history
Privacy or DPO
7
Financial health
Audited accounts, credit report, bank reference
Finance
8
Labour and modern slavery
Modern slavery statement, social audits, sub-tier supplier list
Sustainability
9
Continuity and insurance
Continuity plan, recovery test evidence, insurance certificates
Operations
The right-hand column shapes how the evidence gets stored: nine domains produce six internal reviewers, none of whom needs to see everything.
4. Beneficial ownership: the trap that catches good programmes
If a third party programme fails an audit, ownership is usually where. Screening a company name against sanctions lists is easy and mostly automated. Establishing who actually owns and controls that company is neither, and it carries strict liability.
The reason is aggregation. Under the OFAC 50 percent rule, any entity owned 50 percent or more, directly or indirectly and in aggregate, by one or more blocked persons is itself blocked, even though its own name appears on no list, and the EU applies a comparable ownership-or-control test. Aggregate means exactly that: two shareholders at 30 percent each, both linked to the same designated individual, put the counterparty over the line even though neither holding does alone.
Ownership is also hard because registries disagree with each other and with reality. EU anti-money-laundering rules use a 25 percent shareholding as the threshold for identifying an ultimate beneficial owner, so a chain of holdings each sitting just below it can obscure control entirely. Nominee shareholders and jurisdictions with no public registry produce charts that stop before reaching a natural person, and a chart that stops at another company is not an answer.
Finding
How it surfaces
What the reviewer does
Ownership stops at a nominee
Registry extract names a corporate services firm, no natural person
Require a signed UBO declaration with identity documents
Aggregate holdings cross 50 percent
Two shareholders below 50 percent, both linked to one blocked person
Halt payments and escalate to sanctions counsel before onboarding
Chain routes through an opaque jurisdiction
Holding company in a country with no public ownership registry
Commission enhanced diligence locally, or decline the counterparty
Name match without identity match
Screening tool flags a common name with no date of birth
Human adjudication, with the false positive decision documented
Ownership changed after onboarding
Registry monitoring alert or disclosure during a scheduled refresh
Re-run screening and re-paper the contract if control changed
These remedies differ from M&A findings. In a transaction a finding becomes a price adjustment; here there is no middle ground, because a sanctions ownership finding means you cannot transact at all.
5. The regulations that make this mandatory
Third party diligence used to be prudence. It is now a statutory duty in several overlapping regimes, and the overlap is the difficulty: one supplier can sit inside three obligations with three evidence requirements and three deadlines. The anti-bribery regimes came first and remain the most consequential. The US Foreign Corrupt Practices Act reaches conduct by agents, distributors and consultants acting on a company's behalf, and its books-and-records provisions mean an improperly described payment to an intermediary is itself an offence. The UK Bribery Act 2010 goes further with the section 7 corporate offence of failing to prevent bribery by an associated person, a category that expressly covers agents and suppliers. The only defence is adequate procedures, and risk-based due diligence is one of the six principles in the Ministry of Justice guidance, which is the clearest statement anywhere that a documented tiering method is a legal asset.
Sanctions and anti-money-laundering rules add the second layer. OFAC and EU sanctions programmes operate on strict liability, so a good-faith payment to a blocked entity is still a violation, and EU rules require obliged entities to identify beneficial owners against the 25 percent threshold. Financial-sector counterparties face more: DORA has required EU financial entities to keep a register of information on ICT third-party arrangements since January 2025, and NIS2 makes supply chain security a mandatory risk measure. Our bank vendor due diligence checklist covers that version.
Supply chain and human rights legislation is the newest layer and still moving. The German Supply Chain Due Diligence Act has applied to companies with at least 1,000 employees in Germany since 1 January 2024, requiring a documented risk analysis, preventive measures, a complaints procedure and annual reporting, and reaching indirect suppliers once the company has substantiated knowledge of a problem. The EU Corporate Sustainability Due Diligence Directive entered into force in July 2024, and the Omnibus package adopted in February 2026 narrowed its scope to companies above 5,000 employees and €1.5B in net turnover, with transposition due by 26 July 2028. In the UK, section 54 of the Modern Slavery Act 2015 covers organisations turning over £36M or more.
6. The questionnaire is not the deliverable
Most programmes are built around a questionnaire, and most are weaker than they look for exactly that reason. A questionnaire is a set of assertions by the counterparty about itself: it tells you what the supplier says is true. The evidence behind each answer tells you whether it is, and the evidence is what an auditor or an enforcement lawyer asks to see.
The distinction is practical. A supplier ticks yes to ISO 27001 certification, and the certificate, when it arrives, covers a data centre in a different country from the one hosting your data and expired four months ago. Another confirms it has an anti-bribery policy, and the policy is two pages, undated, and has never reached the sales agents who deal with officials. Neither gap shows in a questionnaire response.
So the collection mechanism matters as much as the question set. Evidence arrives as PDFs, certificates and signed declarations, from a counterparty doing it under duress and often without a secure channel of their own. Email attachments are the default and the worst option: they scatter across inboxes, carry no access control on documents the supplier considers confidential, and leave no record of what arrived when. A file request link into a data room for third party due diligence solves that in one step.
Counterparty evidence lands in the supplier folder through a file request link, rather than in five inboxes.
It is worth being honest about where automation stops. Screening tools are excellent at breadth: they check names against hundreds of lists continuously and surface a match within minutes of a designation. What they cannot do is decide whether a match is the right person. Common surnames, transliterations from non-Latin scripts and similar trading names generate alerts only a human can adjudicate, and the adjudication has to be written down. Nor can a tool notice that a SOC 2 scope statement excludes the service you are buying.
7. Ongoing monitoring, fourth-party risk and offboarding
The largest structural weakness in third party programmes is treating diligence as an onboarding gate. The counterparty is screened, approved, and contracted with for six years, during which its ownership changes, its certification lapses, its finances deteriorate and its own subcontractors change twice. The file still shows a clean review, because the review was done in 2023.
Continuous monitoring closes part of that gap and is cheap for the checks that automate well. Sanctions screening should run continuously rather than in batches, because a designation takes effect immediately and a monthly cycle can leave you transacting with a blocked entity for up to 30 days. What does not automate is the evidence refresh: somebody has to notice that a SOC 2 report covers a period ending eleven months ago and request the current one, and that task falls off the list because nothing breaks when it does.
Fourth-party risk is the layer beneath. Your vendors' vendors process your data and hold your uptime, and you have no contract with any of them. The controls are narrow but real: require a sub-processor and sub-supplier list at onboarding, require notice with a right to object before a material sub-processor changes, and flow anti-bribery, labour and security obligations down the chain contractually. Concentration is the part people miss: four vendors on separate contracts are one incident if all four run in the same cloud region.
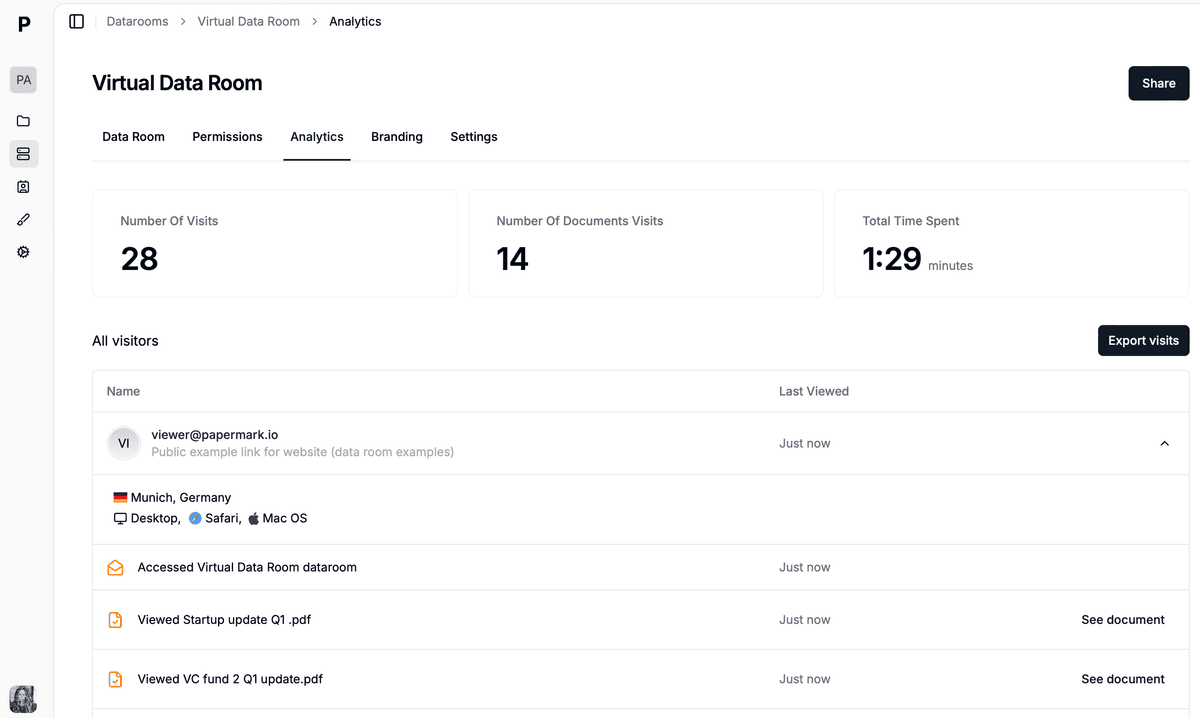
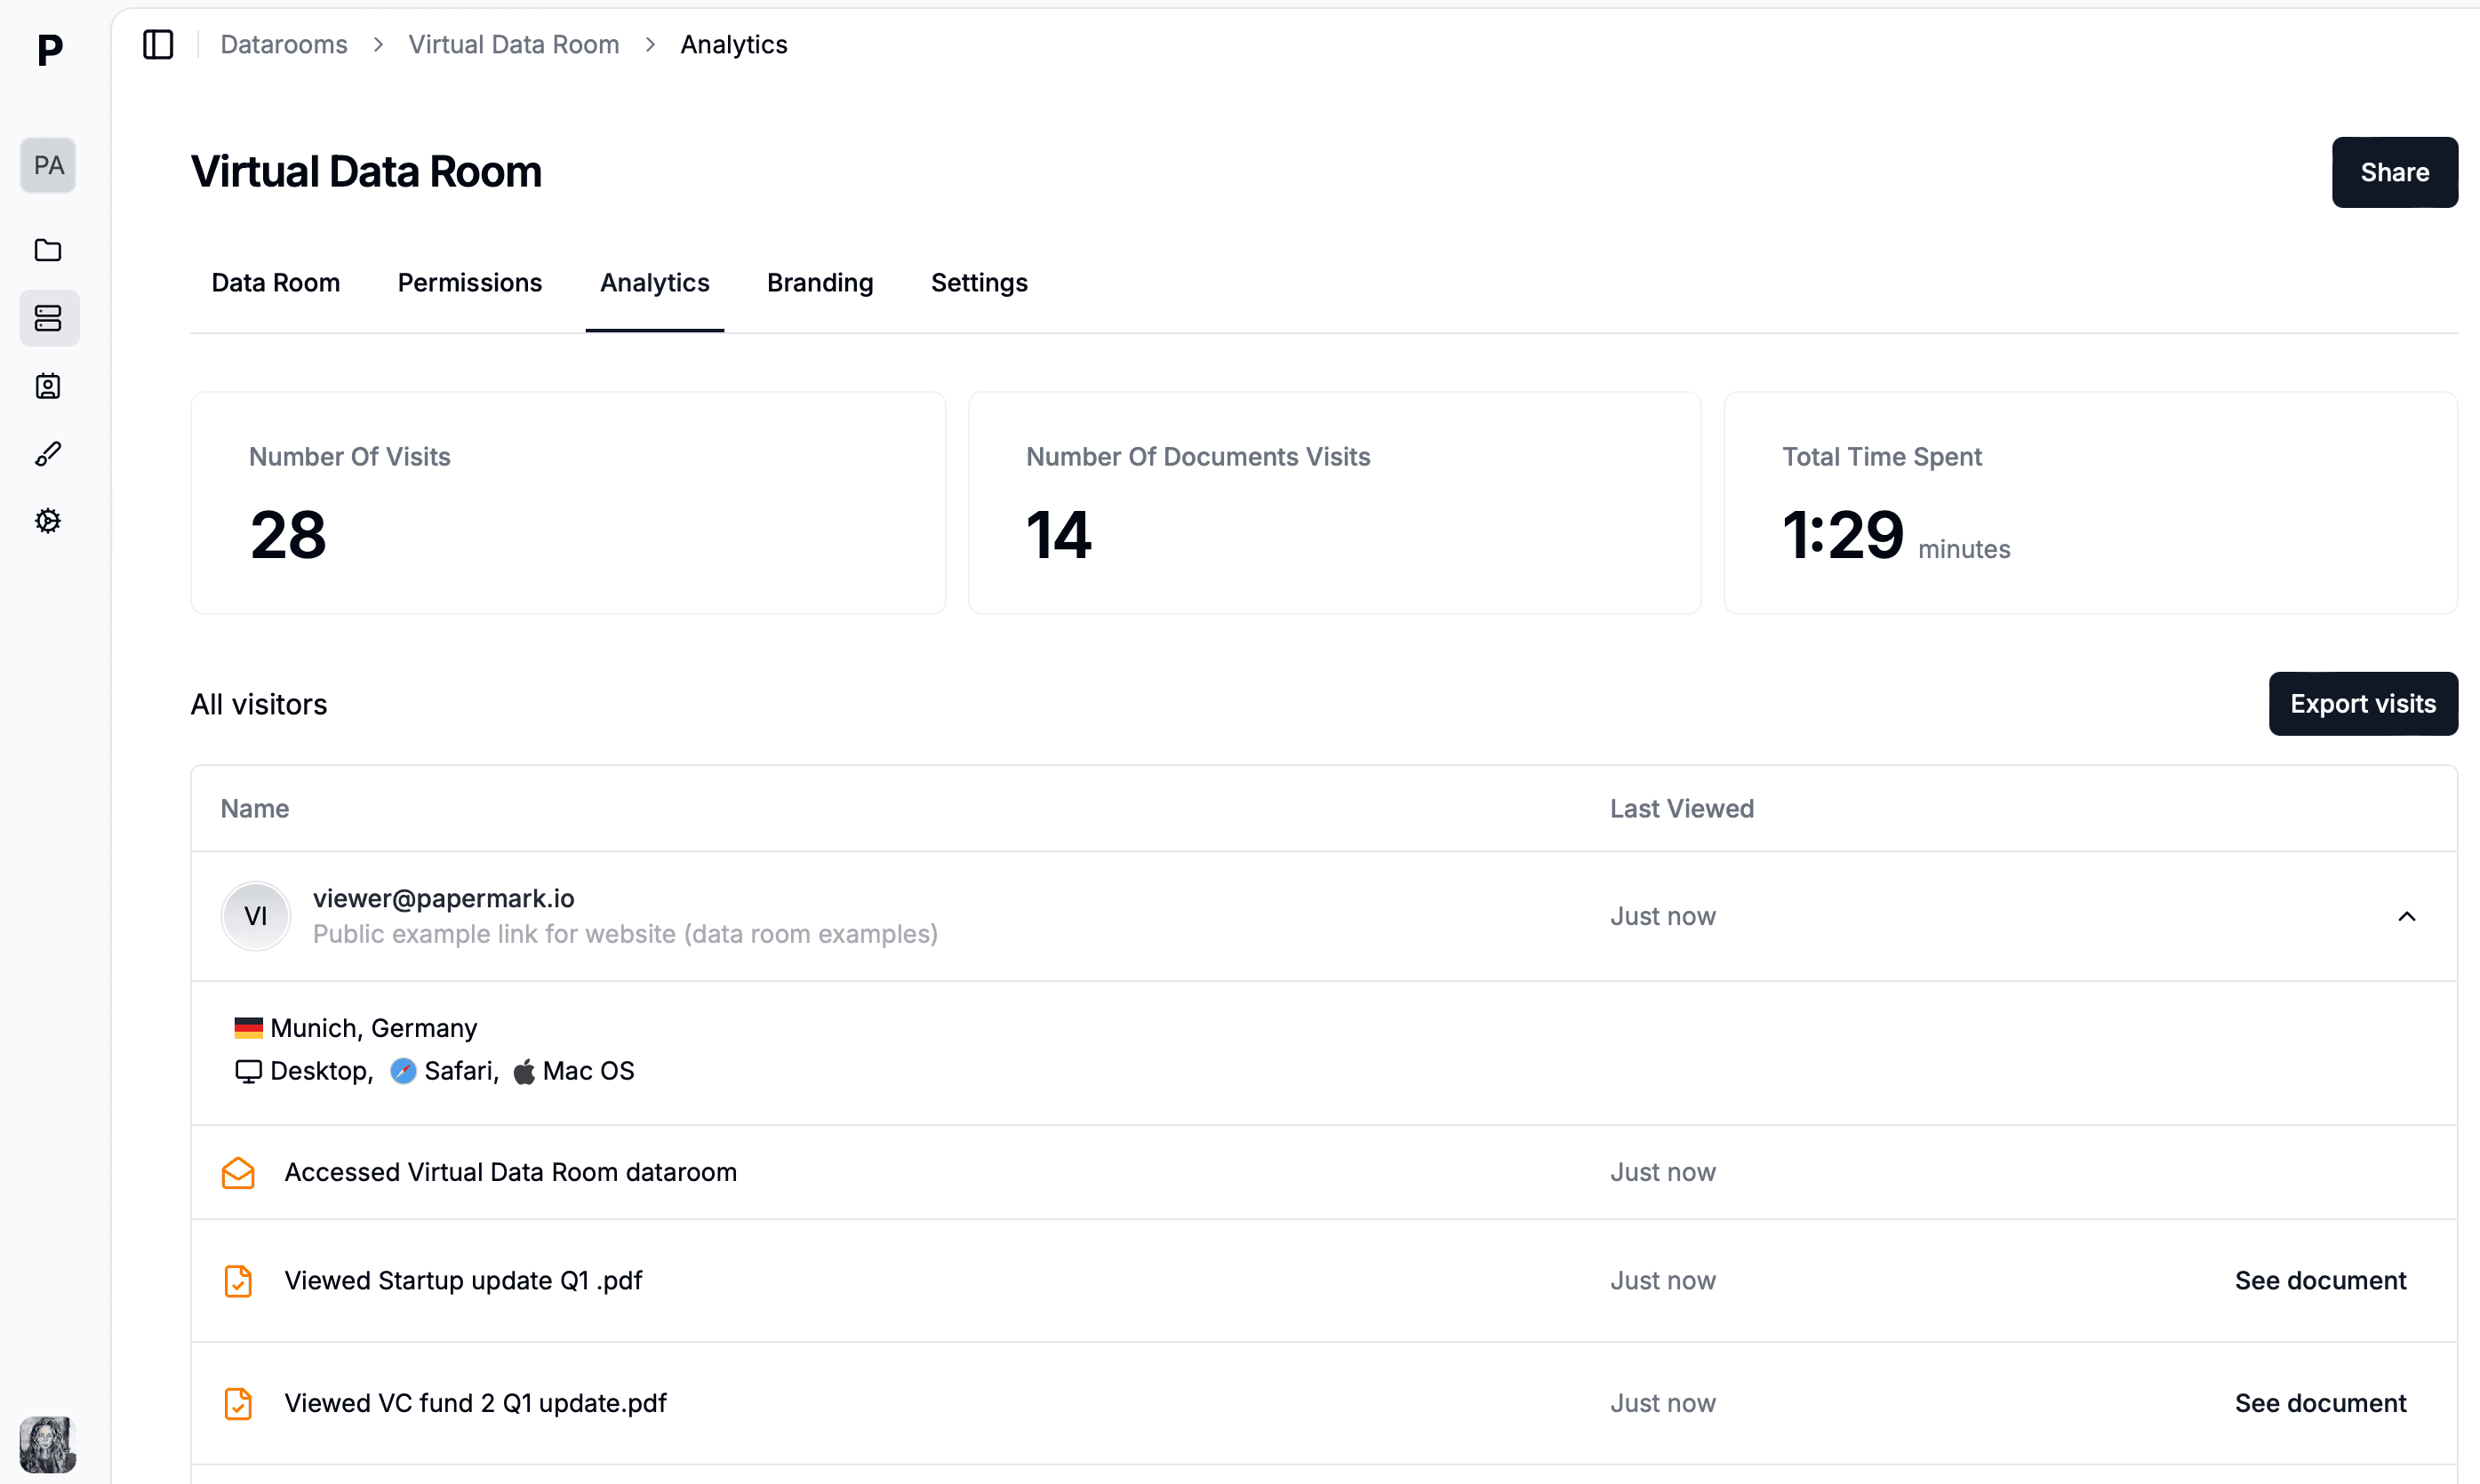
Analytics show which reviewer opened which counterparty file and when, the record an internal audit asks for.
The contract is where findings become enforceable. Audit rights let you inspect rather than rely on the annual questionnaire, certification clauses require the counterparty to keep certificates current and notify you if one lapses, and flow-down clauses push the same obligations to sub-suppliers. A right to terminate for a compliance finding, with no cure period on a sanctions or bribery matter, is what lets you act on what diligence uncovers.
Offboarding is the step nobody budgets for. When a relationship ends, someone confirms that your data was returned or destroyed with evidence, that access was revoked, and that the file is archived for your retention period.
8. Worked scenario: tiering 640 suppliers at Rheinbach Ingredients
Rheinbach Ingredients GmbH is a €410M revenue food ingredients manufacturer with 1,240 employees in Germany, which puts it inside the German Supply Chain Due Diligence Act. It has never run a formal third party programme: procurement approved suppliers on commercial terms, compliance screened names when asked, and the evidence lives in eleven inboxes.
The first exercise is tiering. Across 640 active suppliers, the model places 44 in Tier 1, driven by cocoa, palm oil and spice sourcing from high-corruption jurisdictions plus two customs agents who deal directly with port officials. Another 173 land in Tier 2 on material spend, personal data processing or regulated services. The remaining 423 are Tier 3 and get continuous sanctions screening with a registry check.
Rheinbach Ingredients: supplier population by risk tier
640suppliers
Tier 1, enhanced diligence44 · 7%
High-corruption sourcing and two customs agents
Tier 2, standard diligence173 · 27%
Material spend, data processing, regulated services
Tier 3, screening only423 · 66%
Commodity supply, no data access, low-risk jurisdictions
Worked scenario. The 44 Tier 1 suppliers absorb roughly two thirds of the programme budget, because enhanced diligence costs about ten times a screening-only review.
The findings justify the exercise inside the first quarter. Eleven of the 44 Tier 1 suppliers cannot produce an ownership chart resolving to a natural person. One spice supplier's holding company has two shareholders at 30 percent each, both connected to the same designated individual, putting aggregate blocked ownership at 60 percent and stopping payments under the OFAC 50 percent rule. Neither customs agent has an anti-bribery policy or gifts register.
Year one costs just under €96,000: roughly €1,400 each for the 44 enhanced reviews, €150 each for the 173 standard reviews, and €20 each for the 423 low-risk suppliers. Evidence for the 217 Tier 1 and Tier 2 suppliers goes into a data room with one folder per counterparty and six reviewer links, and the LkSG risk analysis is written from the folder contents rather than from memory.
9. Common mistakes and what the programme costs
The most common mistake is running diligence after the contract is signed. Once the counterparty is engaged, an adverse finding has no leverage behind it: terminating costs money, the sponsor pushes back, and the finding becomes a risk acceptance memo nobody revisits.
The second is tiering on spend alone. Spend is easy to pull from the finance system and correlates poorly with risk. A €9,000 contract with a sales agent who meets government officials is a larger exposure than a €4M contract with a commodity logistics provider in a low-risk country.
The third is scattering the evidence. When an audit asks what was known and when, the answer has to come from a file rather than from reconstruction. Our data room checklist covers how to structure that so the record survives staff turnover.
On cost, published market rates are consistent enough to plan against. A fully automated review runs roughly $200 to $500 per counterparty, adding manual review of the submitted artefacts takes it to around $1,000, and enhanced diligence with a local investigator costs several thousand. Per-review costs fall as volume rises, which is why tiering pays for itself: the saving comes from not running deep reviews on the 60 or 70 percent of the population that does not need them.
Gérez la due diligence avec une data room virtuelle
Aucune carte de crédit requise
Analyses page par page
Documents et dossiers illimités
Gestion des permissions
Filigranes dynamiques
Collecte de NDA
Alertes en temps réel
Personnalisation de marque
Piste d'audit
10. Data room for your third party due diligence
A data room for third party due diligence is a different artifact from a deal room. A deal room opens, fills up, gets read by four parties and closes in twelve weeks. A third party room is permanent, holds one folder per counterparty rather than one per topic, and the traffic runs in both directions: the counterparty uploads evidence, and your internal reviewers read it.
Time is the second difference. Deal documents are read once and archived. Third party evidence is read at onboarding, re-read at every refresh, and produced years later if an enforcement question arises about a supplier you dropped in 2027. The room has to answer who saw what and when, long after the people involved have gone.
Papermark is a secure, fully customizable, and developer-friendly data room built for modern dealmakers, with page-by-page analytics, dynamic watermarking, and transparent pricing (open-source and self-hosting available).
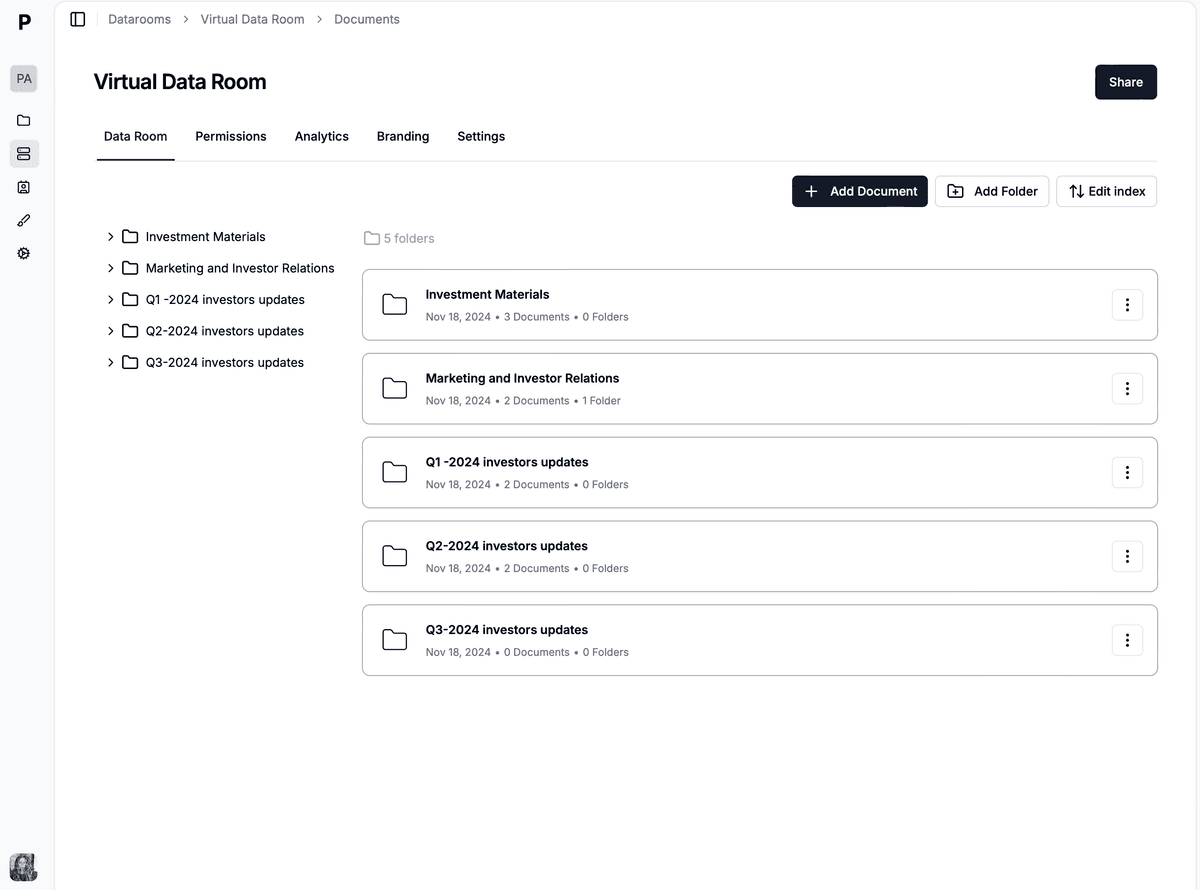
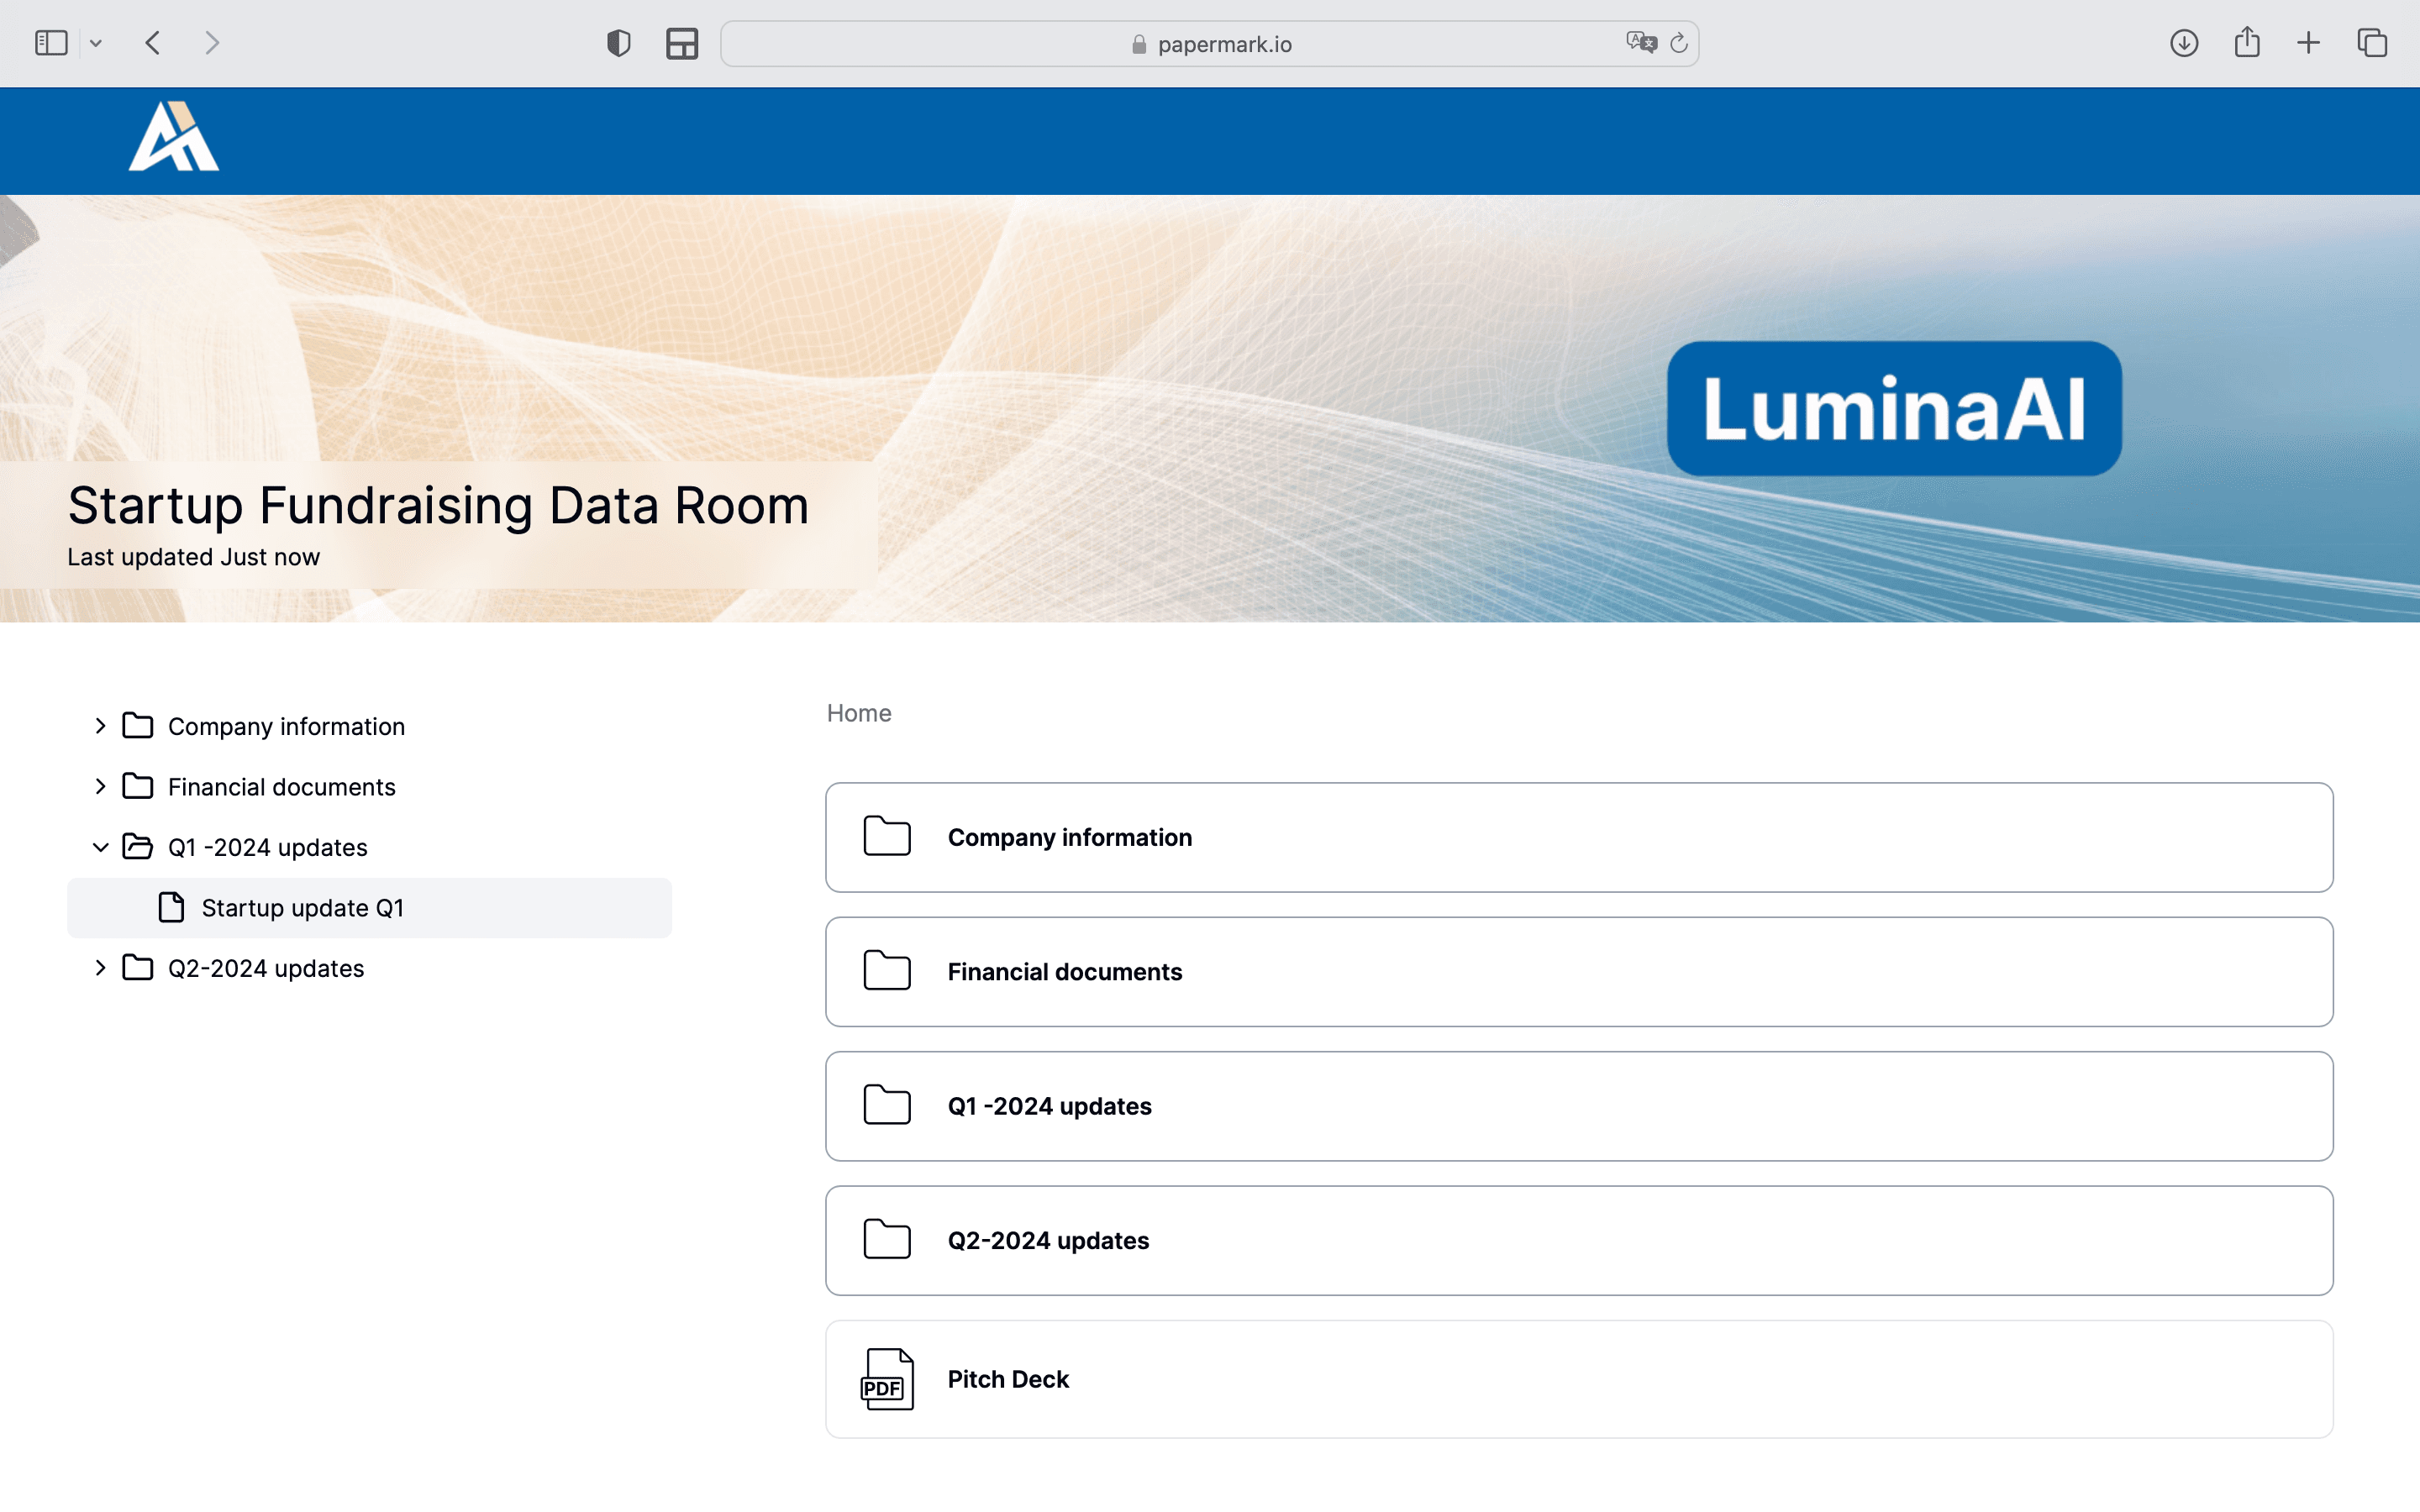
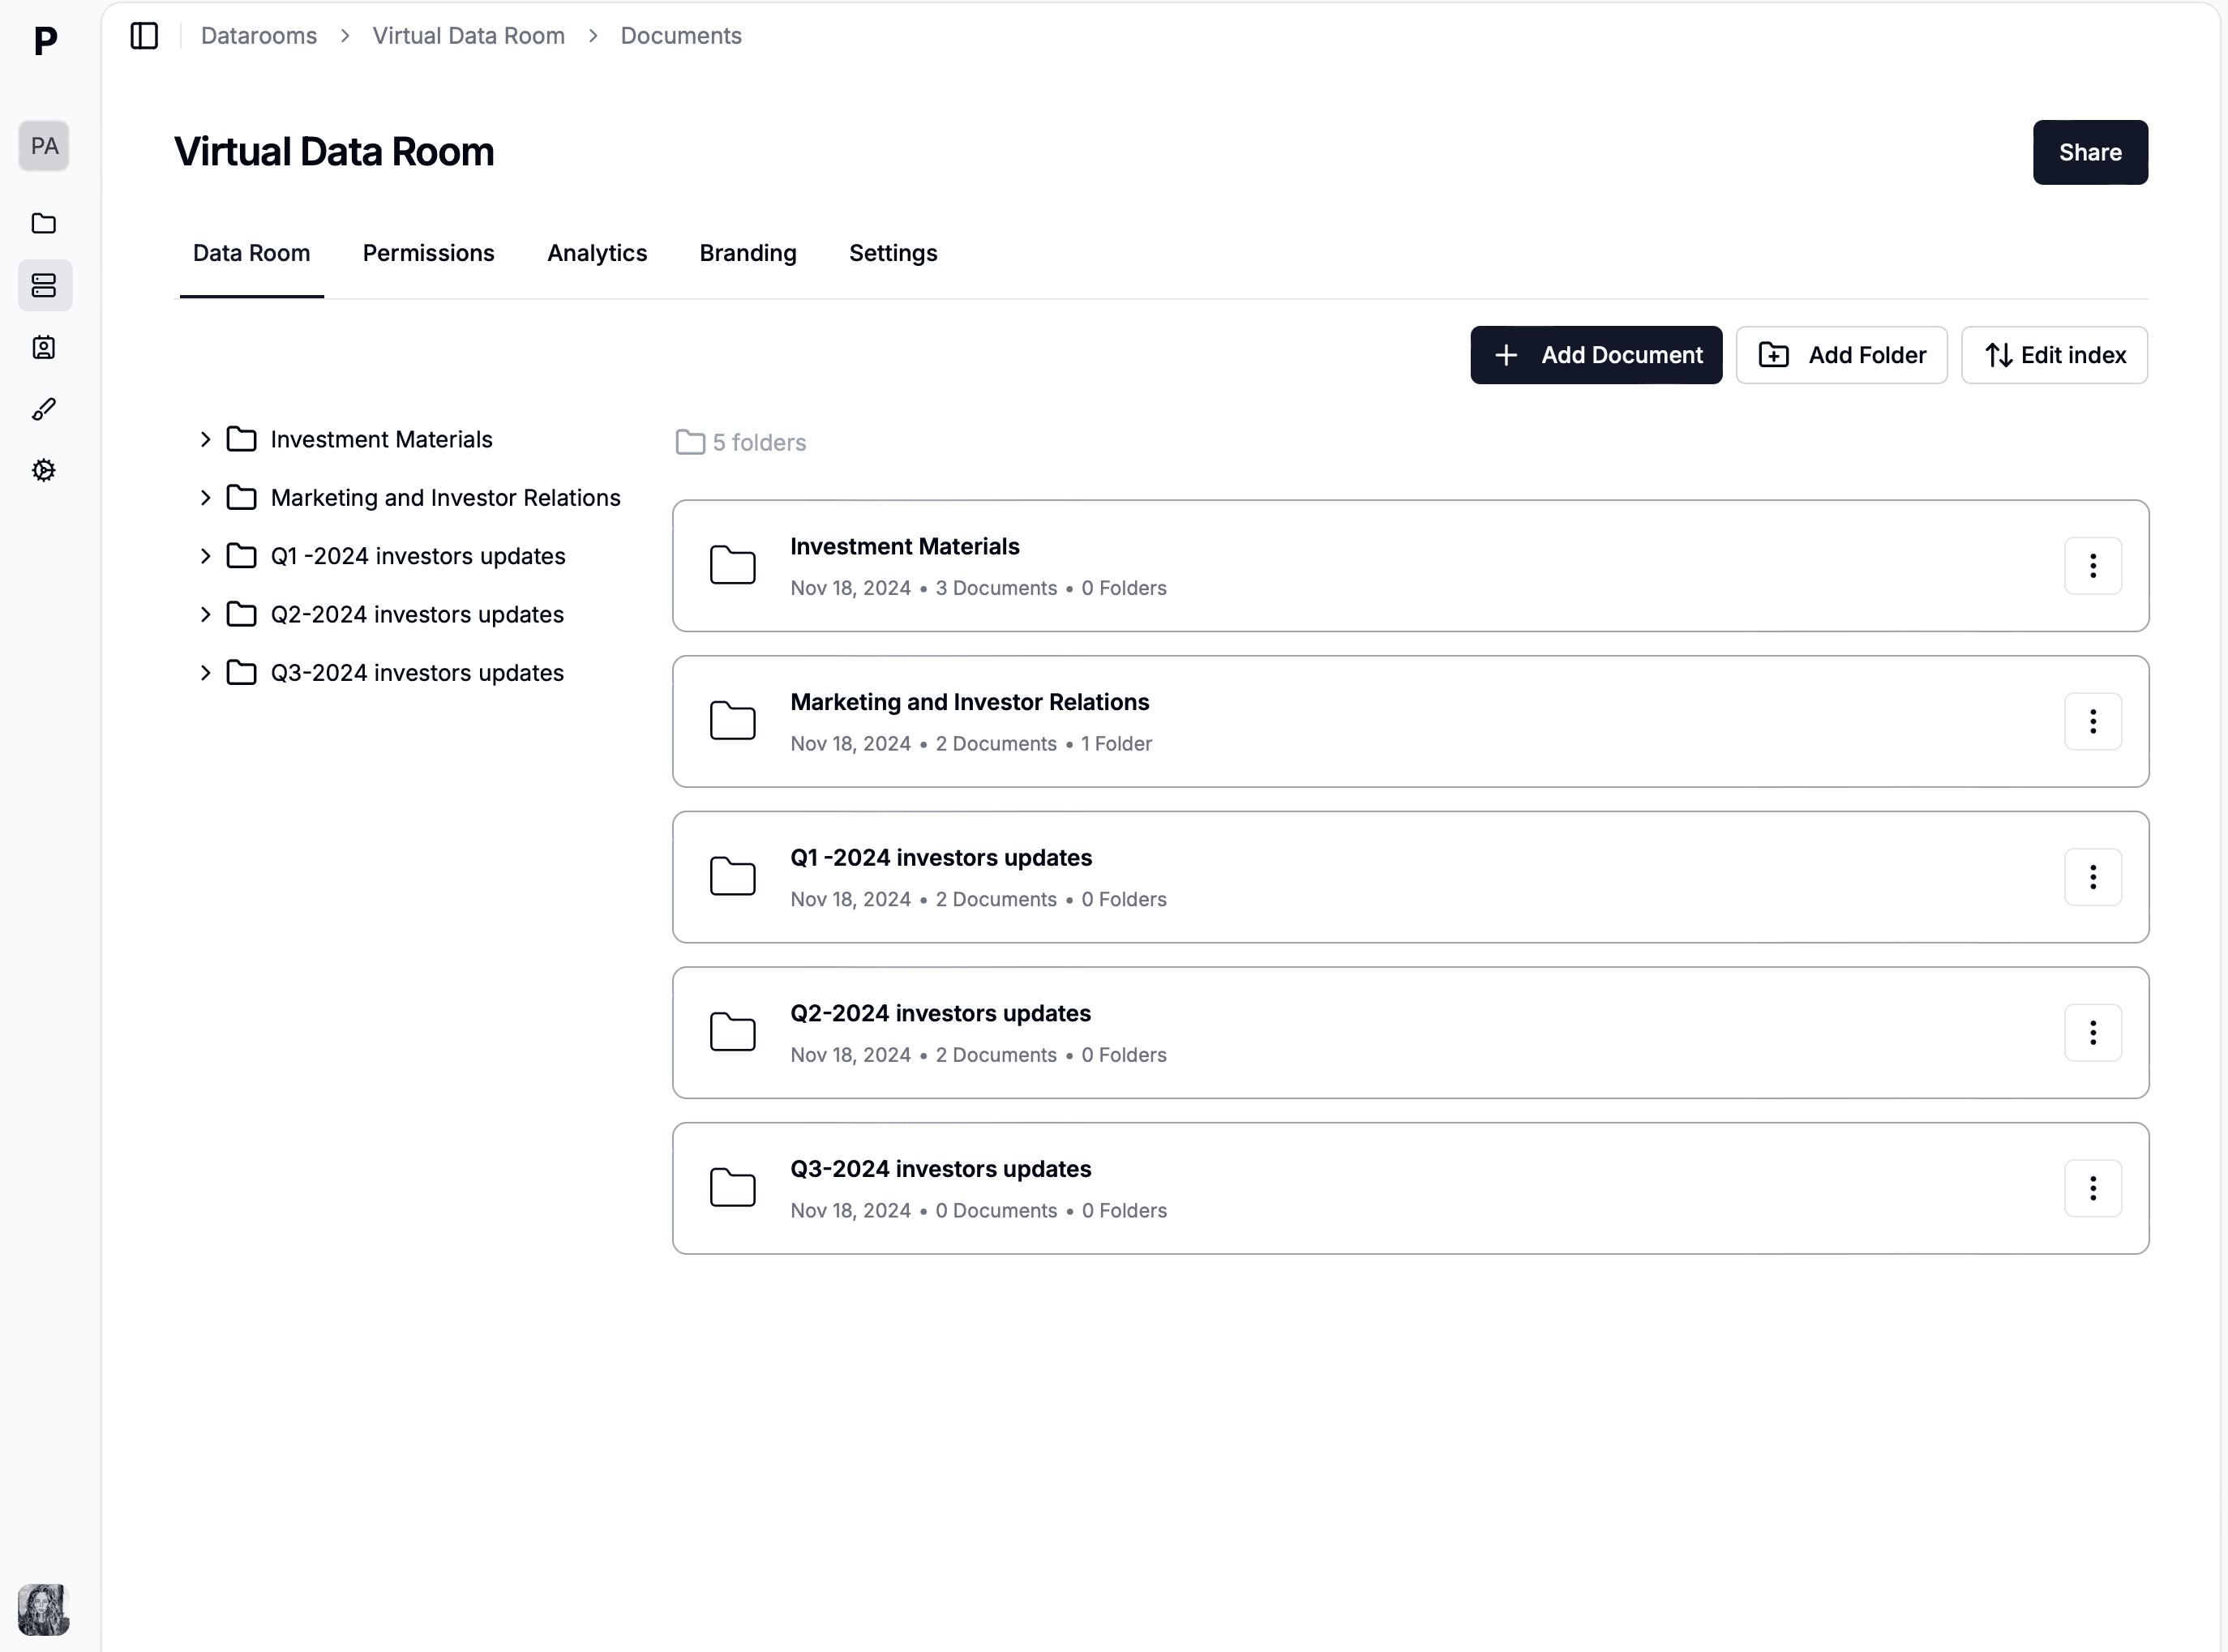
A third party due diligence data room with one folder per counterparty, so permissions and retention follow the relationship.
Why you need a data room for third party due diligence
Questionnaire platforms handle the workflow well and the evidence badly, which is why so many programmes end up with a clean dashboard and an unusable file. Four reasons a dedicated data room for third party due diligence earns its place alongside whatever sends the questions. If you are still choosing, our comparison of the best virtual data rooms covers pricing, permissions and compliance.
The evidence is what gets asked for, not the answers. An auditor does not want your questionnaire completion rate. They want the ISO certificate that was current when the supplier was approved, the ownership chart that resolved to a named person, and the record of who reviewed both. Those are documents, and documents need permissions, versioning and retention, which a workflow tool storing attachments as a side effect of a form submission does not provide.
The flow runs in both directions. You diligence your suppliers, and your customers diligence you. Any company selling into financial services or the public sector spends real time assembling the same pack of certifications and financial statements for every prospect who asks. Keeping it in the same data room for third party due diligence, behind one link with an NDA gate, turns a recurring week of work into a link you send.
Six reviewers need six different views. The nine domains map to compliance, legal, security, privacy, finance and operations, and none of them should see the whole file. A security engineer reading a penetration test summary has no reason to open a supplier's audited accounts. A shared folder gives you one permission set; link-based permissions give you one per reviewer group.
The counterparty must upload without seeing anything. This is the requirement that breaks general-purpose tools. A supplier needs to deposit twenty documents into its own folder and read nothing, including its own previous submissions and anything belonging to another supplier. That is an upload-only permission on a scoped link.
Step 1: build the room by counterparty, then by domain
Create one folder per counterparty and, inside it, one subfolder per domain from the table in section 3. That two-level structure is what makes everything else work: permissions attach at the domain level, retention at the counterparty level, and offboarding means archiving one folder. Tier 3 suppliers get a thin folder with a screening report; Tier 1 suppliers get all nine subfolders.
Upload in bulk by dragging the existing folder tree straight in, and let automatic file indexing on Data Rooms Plus maintain the index as evidence arrives.
Step 2: give each internal reviewer its own link
Third party diligence has more internal readers than a deal has external ones, and access should be narrower rather than wider.
Reviewer
Folders granted
Rights
Compliance analyst
All nine domains, all counterparties
View and download
Security reviewer
Information security, data protection, continuity
View only, watermarked
Legal counsel
Ownership, bribery and corruption, adverse media, contracts
View and download
Finance
Financial health and insurance only
View only
Business sponsor
Their own counterparties, summary folder only
View only
The counterparty
Its own upload folder only
Upload only, no read access
Granular file-level permissions are set per link rather than per user account, so each group gets a link with its own folder scope, email allowlist or domain restriction, and download rule. Nobody has to create an account, which matters when the reviewer opens the room twice a year.
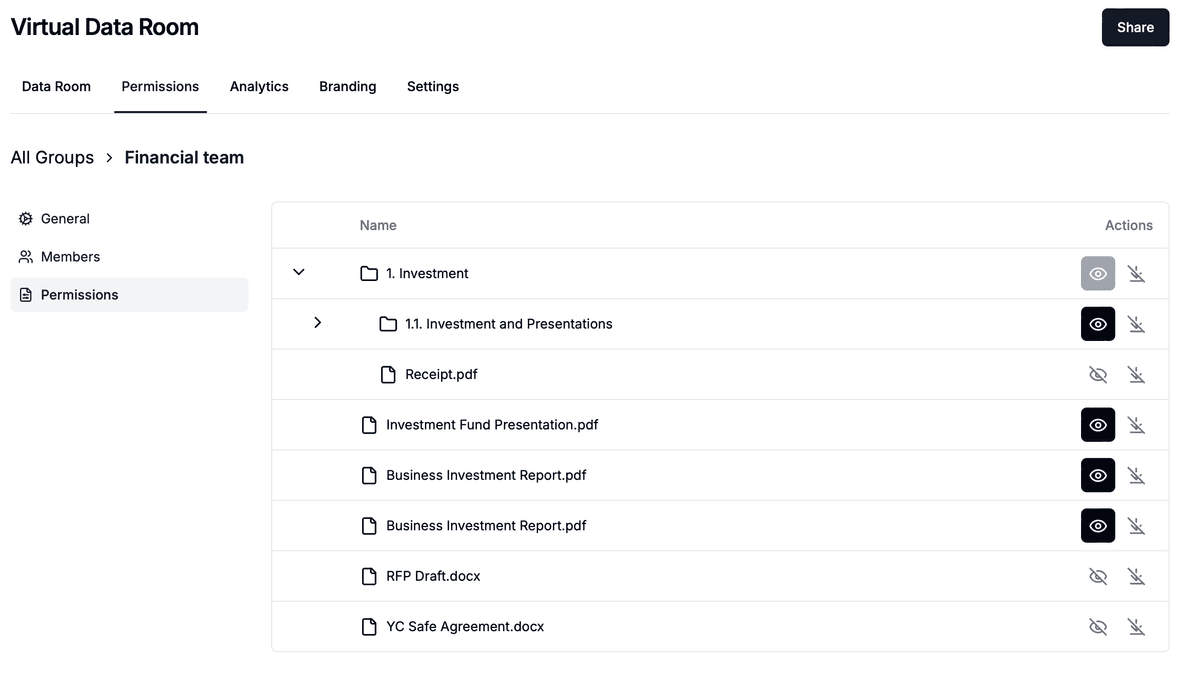
Permissions are set per link, so security, legal and finance see different domains of one counterparty folder.
Step 3: watermark the evidence you did not write
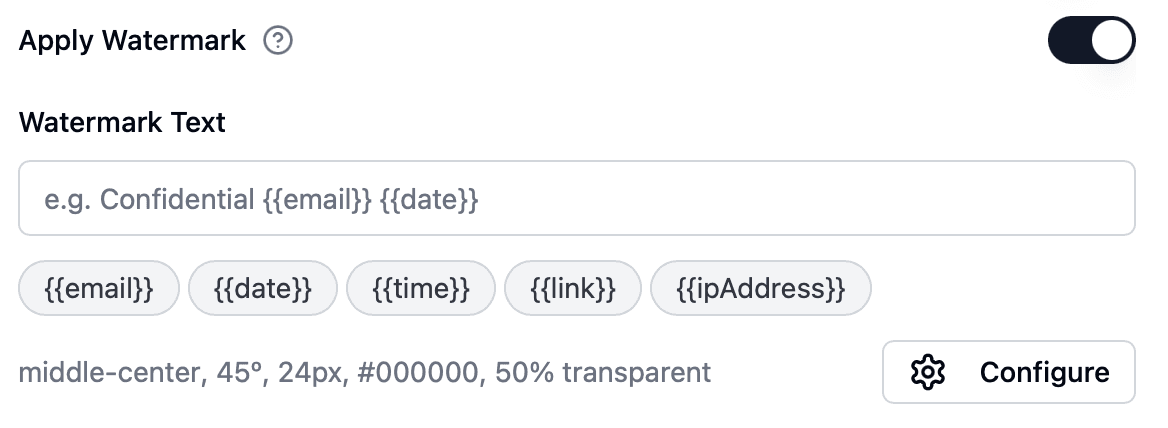
Most of the file belongs to somebody else. A supplier's penetration test summary and audited accounts are its confidential material, handed over under an undertaking that you are the one breaching if it leaks. Set those folders to view-only and enable dynamic watermarking, which stamps every page with the viewer's email, IP address and timestamp as it renders.
The honest limit is worth stating: a downloaded file is legally treated as read, and no platform can recall it. That is why download is disabled rather than discouraged.
Watermark settings stamp viewer email, IP and timestamp onto supplier-confidential documents.
Step 4: collect evidence with file requests, not email
Send each counterparty a link with request files from visitors enabled on its own folder. The supplier uploads certificates and declarations straight into the right place, with email verification confirming who submitted them and link expiration closing the window at the refresh deadline. No attachments, and no confusion about which of three PDFs named soc2-report is the current one.
For questions arising from the evidence, the Q&A module keeps each thread attached to the document that prompted it, with permissions controlling who sees what.
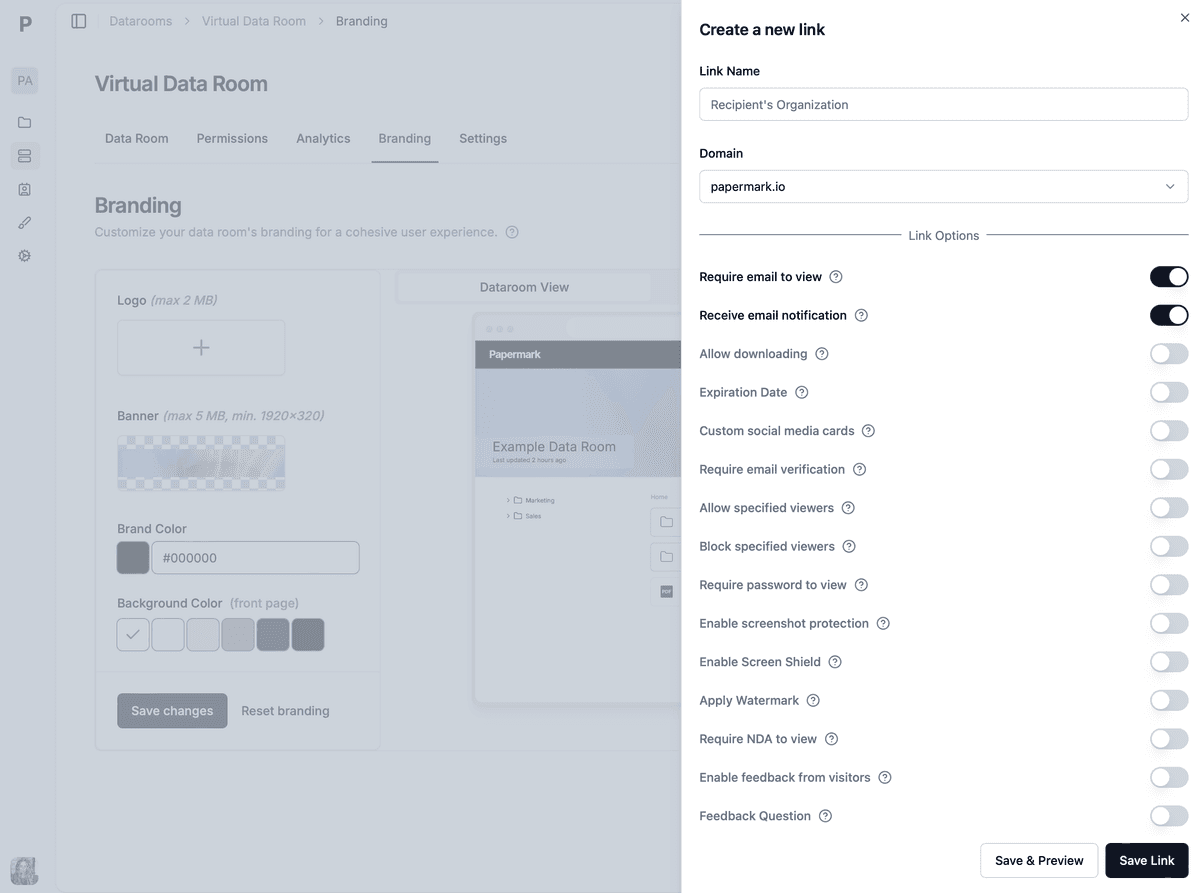
Each counterparty gets an upload link with email verification, an expiry date, and no read access across the room.
Step 5: track the refresh cycle and archive at offboarding
Page-level analytics show which reviewer opened which counterparty document, when, and for how long. That is a management signal: a Tier 1 folder nobody has opened since the last refresh cycle tells you the cadence has slipped, before the auditor does.
The audit log on Data Rooms Plus records access at the visitor level, which is what an internal audit asks for. At offboarding, data room freeze makes a counterparty folder immutable and exports it as an archived ZIP with a certificate. The public API and MCP server are on all plans for teams pushing screening results in automatically.
Papermark is our #1 VDR provider for M&A transactions right now. In two deals we used custom branding, dynamic watermarking, and granular permissions.
The Data Rooms plan is €99/month with a 7-day free trial and includes 3 team members, unlimited data room visitors, unlimited data rooms, unlimited documents, custom domain, dynamic watermarking, NDA agreements, and granular file-level permissions. Data Rooms Plus at €249/month adds 5 team members, the Q&A module, the audit log, automatic file indexing, and SOC 2 Type II. Premium at €549/month adds 10 team members, AI redaction, the API, SSO and whitelabeling. Data Rooms Unlimited at €999/month removes per-seat charges entirely, so teams that add reviewers mid-deal pay one number regardless of headcount, and it carries every Premium capability including AI redaction. Data rooms are unlimited under one subscription, so a programme can run a separate room per business unit at no extra charge.